A new CVE lands. In fifteen minutes you know what to do, and can show you did it.
Ask your AI agent about a new vulnerability with sources attached: Lattice. See Lattice
The method we use to check, analyse and triage a vulnerability, written down so that someone who is not a full-time analyst can repeat it and defend the result. It works through 10 real cases read from the CVE records, the CISA catalogue and the vendors’ own advisories, with 5 scripts run on live data and the templates to keep a record.
What you will be able to do
- Decide in fifteen minutes whether a new CVE matters to your estate, with one of six outcomes and a clock on it.
- Read a CVE record properly, including the fields most people skip and the container a second publisher adds.
- Find the sentence in an advisory that says when the flaw does not apply, and take the work off the list.
- Tell whether your copy is affected, including backported fixes, kernels and libraries you cannot see.
- Fix it, prove it is fixed with evidence a stranger can check, and look for damage from before the fix.
- Explain the decision to a manager or a customer in five lines, and leave a record the next person can read.
A look inside
Three pages of the handbook as they are, so you can judge the level before you register. Press a page to open it full size.
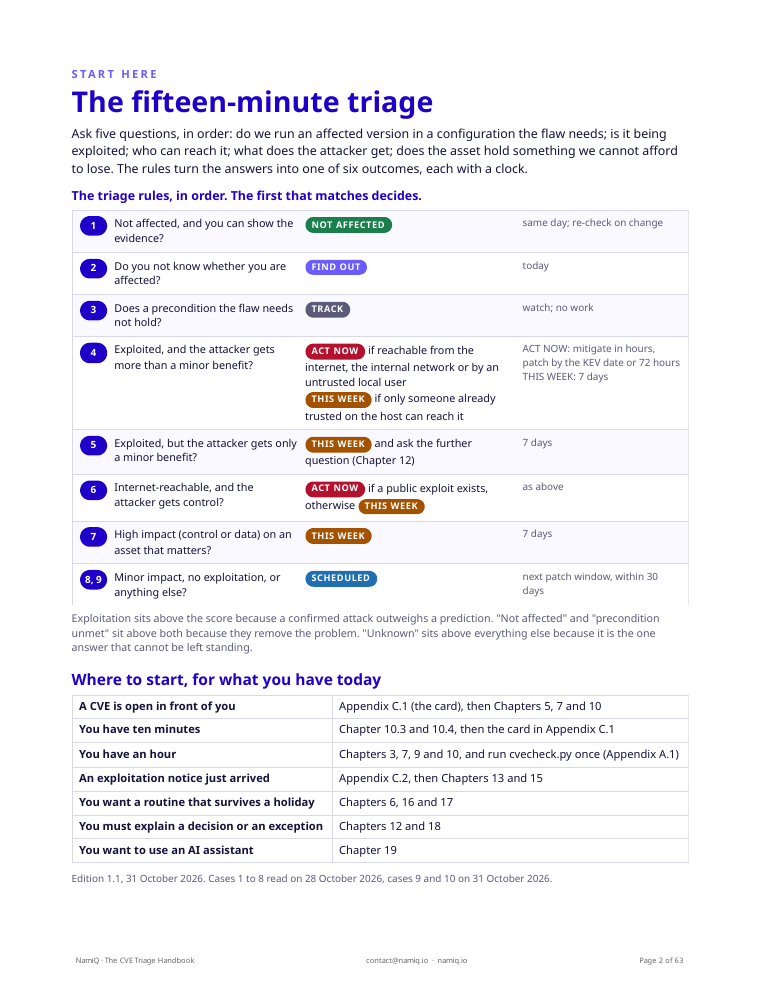
Page 2. The whole method on one page, and where to start for what you have today.
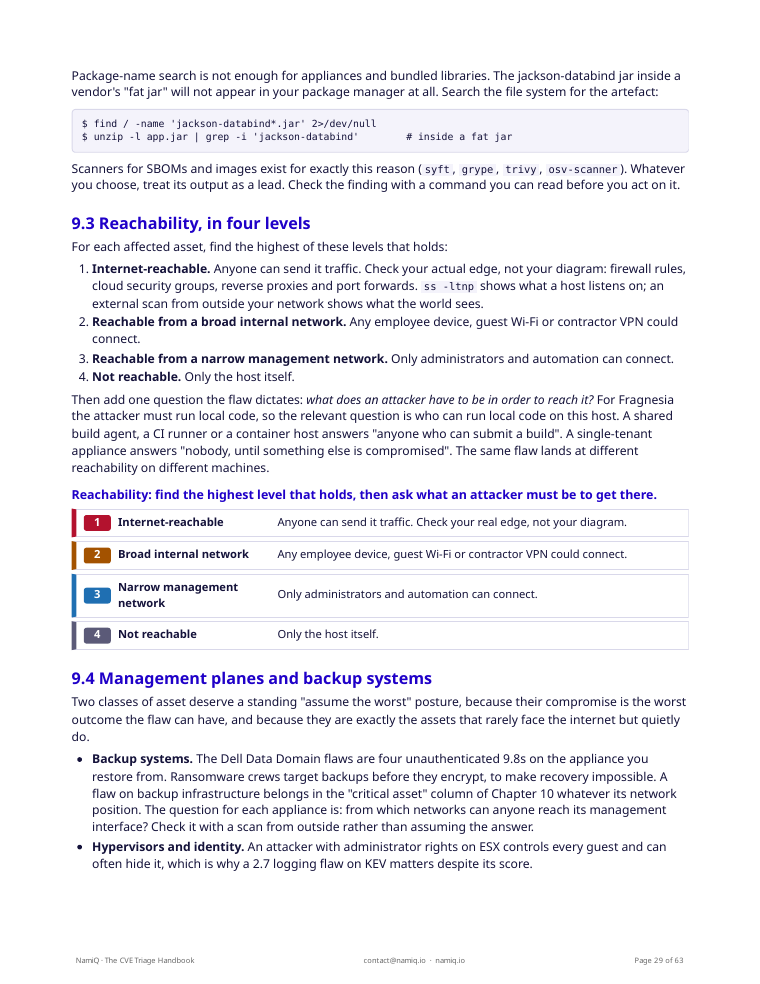
A chapter page. Each chapter opens with what you will be able to do, the one idea to keep, and a ten-minute exercise.
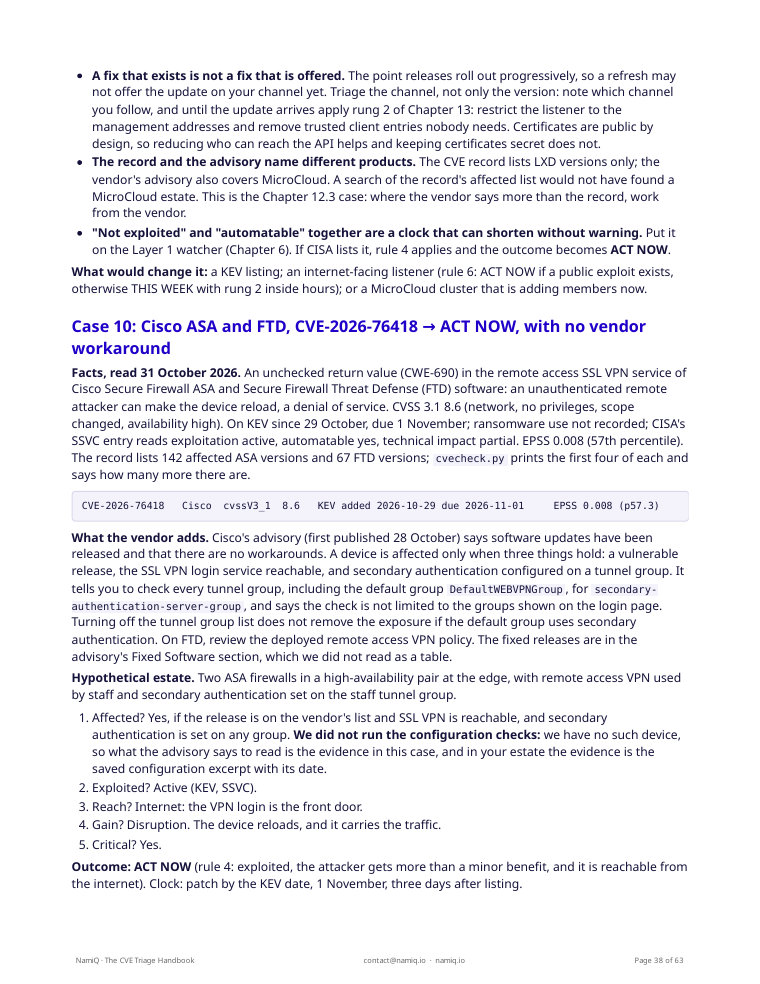
A worked case. Facts read from the sources on a stated day, the five questions, the outcome, and what would change it.
What is in it
19 chapters in seven parts and 5 appendices: 5 scripts, 6 blank templates, 4 cards and checklists, a glossary and the sources. 5 figures, including the whole method on page 2. Every chapter ends with something you can do in ten minutes.
- CheckPart II
Which source answers which question, a field-by-field reading of a real record, and how to notice a change.
- AnalysePart III
Preconditions, version spans, and whether the vulnerable code is reachable on your systems.
- TriagePart IV
Five questions and six outcomes, 10 worked cases and the awkward ones.
- ActPart V
The mitigation ladder, proving a fix, and looking back for damage.
- Run itPart VI
A thirty-minute daily routine, the records and numbers worth keeping, and how to tell people.
The vocabulary, why the feeds disagree, and how to decode a CVSS 3.1 and 4.0 vector. Every step above stands on it.
What to hand an assistant, what to keep, and four questions that work on an assistant or an analyst.
Five scripts, six templates, four checklists, a glossary and the sources.
Where the lookups come from, and how to check a project
The handbook’s method starts from a CVE id. Lattice is the public graph that answers it for an AI agent over MCP; the lattice-scan command line compares an id with what a project declares, or with what a server has installed (its packages, snaps, running images with their operating system and packages, and kernel), and prints evidence for a person. The guide says which of the MCP server, the Claude skill and the command line fits your job. The package is on PyPI and in the signed apt repository.
10 worked cases, 12 CVEs
Instead of invented examples, the book reuses real CVEs from the weeks it was written, each chosen because it breaks a different rule of thumb. The outcomes are our triage judgements on a stated, hypothetical estate, not rulings on any vendor.
Brotli, CVE-2026-111497
Case 1Act now
A library you cannot see, a CVSS 4.0 score, and the highest chance of exploitation in the set.
Linux kernel Fragnesia, CVE-2026-46300
Case 2Depends on who can run code
A local 7.8 on the exploited list: the same flaw lands differently on a shared build host and a single-tenant appliance.
VMware ESX, CVE-2026-41709
Case 3This week, plus an investigation
A CVSS 2.7 on the exploited list, and what it says about whose logs you can trust.
Adobe Commerce, CVE-2026-48356
Case 4Act now
Patched in July, exploited in October: why triage once is not enough.
jackson-databind, CVE-2026-110879
Case 5Depends on configuration
An incomplete fix: the upgrade you already did may not cover you.
Apache Kafka Connect, CVE-2026-115644
Case 6Not affected, if the check says so
A flaw that exists only when you configured something, and the one-line check that proves it.
MLflow, CVE-2026-116692
Case 7Depends on three facts
Exposure that needs three conditions at once.
Dell Data Domain, DSA-2026-416
Case 8This week
Four 9.8s on the appliance you restore from, published four weeks before the CVE feed, and the firewall change that comes first.
Canonical LXD, CVE-2026-112816
Case 9This week
A 10.0 that is not exploited, a fix that may not be offered to you yet, and a record and an advisory that name different products.
Cisco ASA and FTD, CVE-2026-76418
Case 10Act now
Exploited, with a low prediction score, a precondition you must check in every group, and no vendor workaround.
Who it is for
The one person who is “the IT person”
You look after everything, security included, and cannot read every advisory. Start with the one-page start and the fifteen-minute card.
The security or platform engineer
You own the patch process and need it to be fast, consistent and auditable. The method as rules, as code, and as a routine.
The leader who signs off
You approve exceptions and explain decisions afterwards. The triage model, the edge cases, and how to tell people.
What makes it different
Worked on real records
Says what it could not read
Questions
- Is it free?
- Yes, with a work email. We send one confirmation; when you press its button, the page you land on has the handbook, and the same link stays in the email.
- What do you do with my email?
- We keep what you send in the form: your name, work email and company, plus the role, phone number, postal code, device count and message if you add them. A person at NamiQ reads your registration. You can unsubscribe or ask us to delete it at any time.
- Do I need special tools?
- No. The method is on paper. The five scripts are optional, written in Python with the standard library only, and fetch public data. They do not find affected systems on your estate.
- How current is it?
- Edition 1.2, 2 November 2026. The cases were read from the CVE records, the CISA catalogue and the vendor advisories on the day each case states. The method and the rules are stable; new cases appear as notes in Insights as they happen.
- Can I share it?
- Unaltered, with attribution. The cover says so.
Get the handbook
Register with a work email. We send one confirmation; when you press its button, the page you land on has the handbook, and the same link stays in the email. A person at NamiQ will also read your registration.
We keep your name, work email, company and role. Nothing else. Privacy · Unsubscribe or delete